Study · September 2026
Why DijiUni?
This study is in two parts: the first introduces DijiUni and its benefits in general terms, while the second sets out, for institutions and experts, the regulatory basis, the problems observed in the field and the solution map, together with their sources.
Skip to the detailed studyOverview
What is DijiUni?
Through their continuing education centres, universities run certificate programmes for participants of all ages and award a certificate to those who complete them successfully. Today these certificates are largely issued in print or as electronic files, so an employer wishing to confirm that one is genuine often has to contact the issuing institution separately.
DijiUni presents these certificates as digital badges (electronic credentials that can be shared online and checked for authenticity at any time). Each badge is kept securely in its holder's digital wallet, a personal online account managed by the holder alone. Anyone wishing to examine a certificate can verify it within seconds, without contacting the issuer, and confirm that it is genuine, unaltered and still valid.
By way of comparison
Much like the verification code on a bank receipt, the code printed on every badge allows anyone to confirm the document's authenticity with ease.
Just as an identity card belongs to its holder, a digital badge belongs to the person who earned it, and only the holder decides where and with whom it is shared.
A printed certificate can easily be reproduced, whereas a digital badge cannot be forged, as it carries the issuing institution's electronic signature. Should even the smallest change be made to the document, the signature is invalidated and the system detects this immediately.
Why now?
Through two regulations introduced in 2026, the Council of Higher Education (YÖK) required certificates for short training programmes to be issued digitally and in a verifiable form. Accordingly, programmes of Continuing Education Centres (SEM) starting on or after 1 October 2026 will be submitted for YÖK approval, and certificates of approved programmes will be verifiable through the e-Devlet Gateway, Turkey's official e-government portal.
DijiUni was developed to provide the infrastructure these regulations call for to every higher-education institution from a single point, sparing each university from having to build it independently.
Who benefits, and how?
Certificate holders
Holders keep all the badges they earn securely in their personal digital wallet, so certificates can no longer be lost or damaged. A badge can be shared with an employer in a single step or added to a profile on the professional network LinkedIn. When credit recognition is sought at another university, the badge serves as evidence that carries all the required information. These services are free of charge for holders.
Universities
Universities manage the issuing process from a single system, in line with the regulations. Who approved each certificate, and when, is kept on record, and a certificate issued in error can be revoked in a single step. There is no longer any need to develop or maintain separate software for e-Devlet queries.
Employers and institutions
Employers and public bodies no longer need to correspond with the issuing university to confirm that a certificate is genuine. It is sufficient to enter the code on the certificate on the verification page or to scan the QR code with a smartphone. The result appears within seconds in a clear and readable form, and no registration is required.
How does it work?
1. Preparing the certificate
Once the programme has been completed successfully, the university prepares the badge and notifies the participant by email. No prior registration is required of the participant at this stage.
2. Adding it to the wallet
By following the link in the email, the participant adds the badge to their digital wallet. No password is needed, as identity is confirmed through the email address.
3. Sharing and verification
The badge can be shared in a single step. Anyone wishing to examine it need only enter the code on the certificate on the verification page; if the certificate is valid, a green “Valid” notice is displayed.
Frequently asked questions
- Is there a charge for the service?
- The digital wallet and verification services are free of charge for certificate holders and for those who verify certificates. Universities use the system through an institutional subscription.
- Is it necessary to be a student?
- No. Anyone who takes part in a university's certificate programmes can receive a badge, including employees, graduates and participants from outside the institution.
- What happens if a certificate is lost?
- Because the badge is stored permanently in the digital wallet, it cannot be lost, and it can be downloaded again at any time by signing in with the email address. The university also retains the certificate record for the period set out in the regulations.
- Can it be used on mobile devices?
- Yes. The system works fully in a smartphone's web browser and does not require any app to be installed.
- What if my institution does not use DijiUni?
- Since badges are prepared by the university that issues the certificate, the institution must have joined the system. You are welcome to recommend DijiUni to your institution's continuing education unit.
- Can my certificate be viewed on e-Devlet?
- If your university has enabled this service, your certificate can be checked on the e-Devlet Gateway using its document number. e-Devlet does not store the certificate itself; the query is forwarded to the issuing university's system, which provides the answer.
Detailed layer
Detailed study: for institutions and experts
Certified training documents are issued today as paper or PDF, and confirming that one is genuine usually means contacting the issuing institution.
In 2026 YÖK changed this with two regulations: the Micro-credentials Procedures and Principles require the certificate to be a verifiable badge created in a digital wallet, and the SEM certificate regulation requires programmes to be approved by YÖK and certificates to be checkable on e-Devlet.
DijiUni provides the infrastructure these regulations call for, for every university, from a single place. The sections below trace each claim, with its source, from problem to solution.
Why now
Regulatory timeline
Six regulations and decisions point to the same infrastructure need. In date order:
Early 2025
Sanayi ve Teknoloji Bakanlığı Dijital Rozet Platformu (Ministry of Industry and Technology Digital Badge Platform)
An institution-agnostic badge platform for technology training was introduced to universities. It was not made mandatory as the YÖK micro-credential wallet, and it has no university-specific programme, YÖKSİS or EK-1 workflow.
Source:Digital Badge Platform (opens in a new tab)Ankara Univ. notice (opens in a new tab)
21 June 2025
Presidential Circular 2025/10 — digital accessibility
Websites and mobile apps must conform to WCAG 2.2. Public bodies were given one year to comply, and 2026 is marked as the start of audits. As universities are public bodies, verification and wallet screens fall within scope.
18 February 2026
KVKK Board principle decision 2026/347 (Personal Data Protection Authority)
The privacy notice and the explicit consent text must be issued separately; they cannot be merged into one text. Enrolment, wallet and sharing steps in the certificate process must each respect this separation.
10–23 June 2026
YÖK Mikro Yeterlilikler Çerçevesine İlişkin Usul ve Esaslar (Procedures and Principles on the Micro-credentials Framework)
Published on the YÖK website on 10 June and announced publicly on 23 June. It governs how short courses are certified and converted into credit.
- Art. 4-c
- Digital wallet: a platform where certificates are stored, managed and shared securely, portably and under the user's control.
- Art. 6-g
- Learning outcomes and credit are recorded in a digital badge created on a digital wallet platform, verifiable and aligned with international standards.
- Art. 8 · EK-1
- The certificate carries 11 minimum fields: identity, course title, institution, date, learning outcomes, ECTS, TYÇ level, assessment method, mode of participation, success criteria, quality assurance.
- Art. 9
- When external training is recognised, trainer qualifications and process records must be traceable and provable; the university is responsible for verification.
- Art. 10
- Micro-credential credit may be at most 10% of the graduation workload; at most 50% of credit-bearing courses may be online.
Source:YÖK Procedures (opens in a new tab)YÖK announcement (opens in a new tab)
2 July 2026
YÖK letter to universities — SEM certificate programmes
Certificate programmes of Continuing Education Centres (SEM) were brought under central review against common quality criteria. The stated reasons were certificate inflation, fake documents and disputes over content and duration.
Source:AA (opens in a new tab)memurlar.net (opens in a new tab)
1 October 2026
In force
SEM regulation in force
All SEM programmes starting from this date are submitted for YÖK approval through YÖKSİS (Birim İşlemleri → ABAYS → Başvuru → Sertifika Programı Başvuru). The application is made by the Certificate Programme Application Officer designated by the university's HR department. Certificates of approved programmes can be checked on e-Devlet.
Source:AA (opens in a new tab)memurlar.net (opens in a new tab)ogretmenlersitesi (opens in a new tab)
Problems in the field
What goes wrong in the certificate process today?
The problems below are drawn from YÖK's stated reasons, university SEM directives and institutional practice.
01Fake and forged PDF certificates
A PDF or scanned certificate can be edited in minutes; logo, signature and stamp can be copied exactly. The naked eye cannot tell the difference. YÖK explicitly lists fake documents among the reasons for the SEM regulation.
02Verification by phone and email
To confirm a certificate, an employer or public body calls the SEM or sends a letter. The answer can take days and never comes outside office hours. Most of this correspondence is not recorded.
03Every university has its own verification page, or none
Where a verification page exists, the address, format and query fields differ. Where it does not, correspondence is the only route. Verifiers must learn a separate path for every institution.
04Lost certificates and the reissue burden
A person who loses a certificate must apply in writing; some directives require a newspaper notice. The EGESEM directive states that no new certificate is issued after the 10-year retention period. Every request creates manual work for SEM staff.
Source:EGESEM Directive (opens in a new tab)İTÜ SEM Directive (opens in a new tab)
05Certificates added to LinkedIn cannot be verified
A certificate on a profile is just a title and an image; the link usually points to a file, not the institution's record. Yet YÖK aims for badges to serve as global proof on networks such as LinkedIn.
06Missing evidence in recognition requests
Someone seeking credit at another university must prove the EK-1 fields and process records (Art. 9). A flat PDF does not carry learning outcomes, assessment method and trainer details in a provable form. The committee falls back on correspondence.
07The 11 EK-1 fields get lost in free text
Learning outcomes, assessment method, mode of participation and quality assurance are often not printed at all, or appear as free text. Such information cannot be read or compared by machines, and ECTS is calculated by hand.
08Every SEM commissions its own e-Devlet software
An e-Devlet query needs the institution's own query service. Each SEM has it built, hosts it and maintains it under the TÜRKSAT protocol on its own. The same work is repeated at every institution.
09No link between the YÖK approval number and the certificate
After 1 October 2026 a SEM certificate must rest on a YÖK-approved programme. The approval number is typed in by hand or left out, and nothing prevents a certificate being issued from an unapproved programme.
Source:AA (opens in a new tab)
10National ID numbers circulate in the open
The Turkish ID number (TCKN) is printed on the certificate and travels wherever the certificate is shared. KVKK's TCKN guide calls for less intrusive methods; an open ID number on a shared document conflicts with that principle.
11Approval and signature chains are off the record
Depending on the document type, the coordinator, SEM director and rector may all need to sign; the İTÜ SEM directive requires three signatures on a certificate. Signatures are gathered on paper or by email, and who approved when cannot be traced later.
12Attendance and pass thresholds differ between institutions
Attendance is 70% in one directive and 80% in another; the pass mark may be 70 out of 100. Thresholds are applied by hand in spreadsheets, with a high margin for error. The table below compares three directives.
Source:EGESEM Directive (opens in a new tab)İTÜ SEM Directive (opens in a new tab)ODTÜ-SEM Regulation (opens in a new tab)
13Revoked certificates stay in circulation
Even when a wrongly or improperly issued certificate is withdrawn, copies already distributed continue to look valid. There is no way to tell everyone holding it that it has been revoked.
| Rule | İTÜ SEM | ODTÜ-SEM | EGESEM (Ege Univ.) |
|---|---|---|---|
| Attendance | ≥ 70% | ≥ 80% | Participation ≥ 70% · Certificate ≥ 80% |
| Pass mark | Not specified in directive | Set by programme unit | ≥ 70 out of 100 |
| Signatories | Certificate: Rector + Director + Coordinator | Not specified in directive | EGESEM Director |
| Lost certificate | Reissue after newspaper notice and confirmation | Not specified in directive | Written application; not reissued after 10 years |
Source:İTÜ SEM Directive (opens in a new tab)ODTÜ-SEM Regulation (opens in a new tab)EGESEM Directive (opens in a new tab)
What was built
The system's backbone
Each part answers at least one of the problems above directly. Technical names appear in monospace under each item.
One verification address
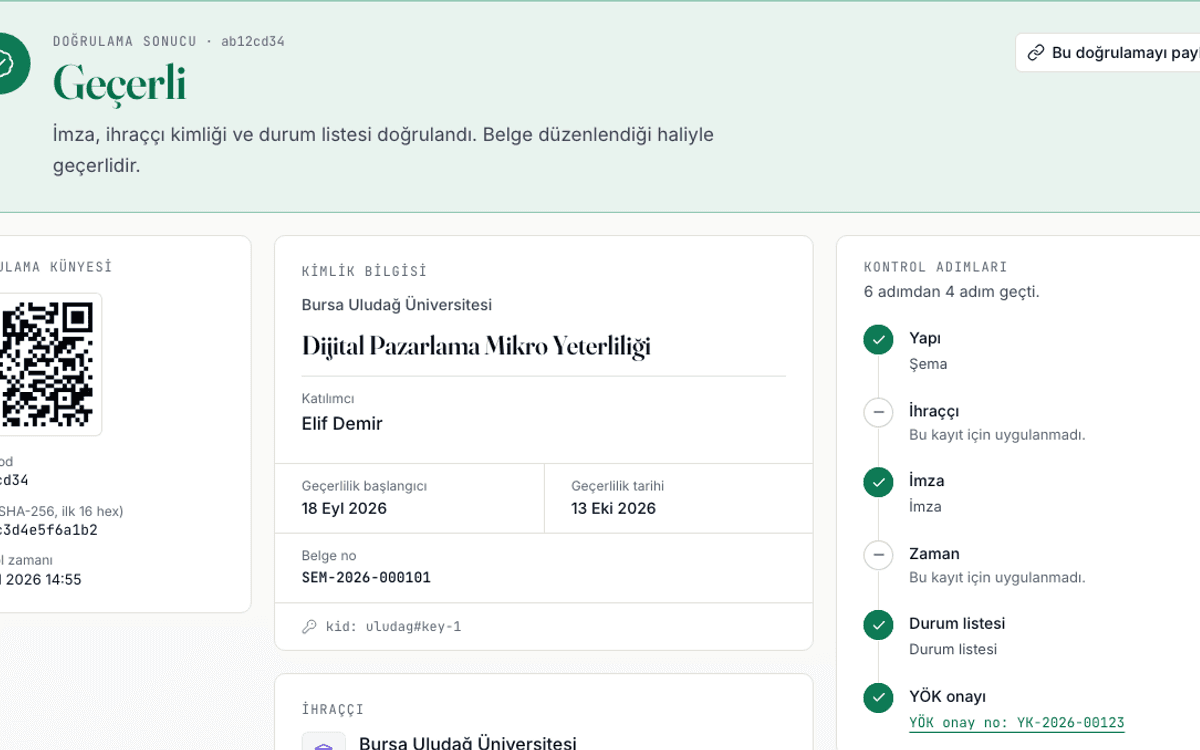
Certificates from every institution are verified at the same address: by short code, certificate link, QR or file (PNG, SVG, PDF, JSON). Software can use the verification API. If the name is hidden, the verifier can confirm identity with the birth date or the last 4 digits of the national ID.
dijiuni.com/verify · POST /api/v1/verify
Signed digital badge and certificate, together
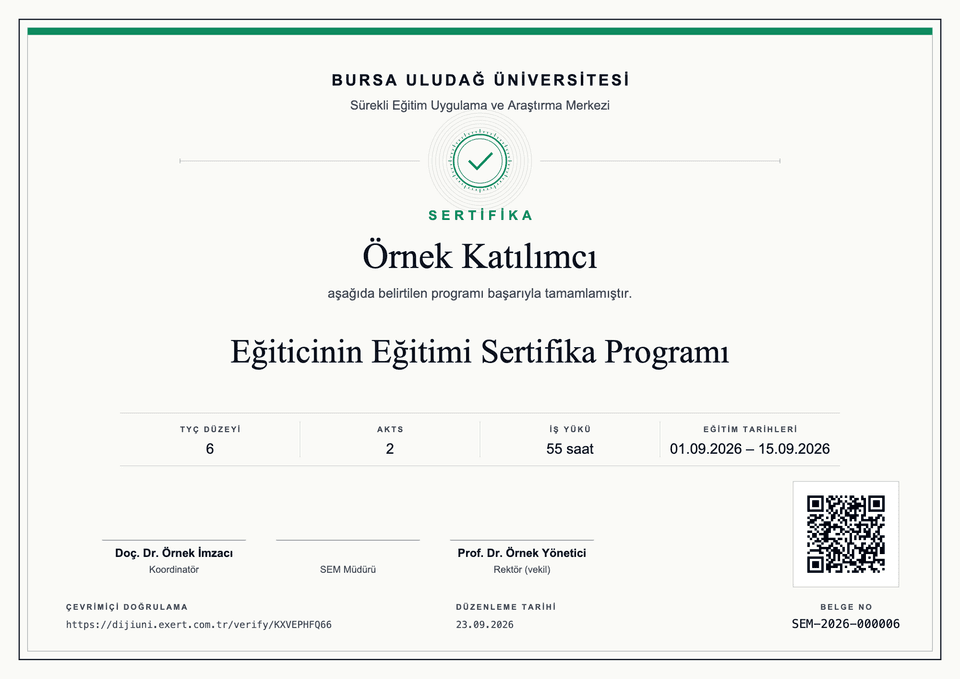
Every certificate is signed with the institution's key to the Open Badges 3.0 and W3C Verifiable Credentials 2.0 standards. The same signed record produces both a badge image (PNG/SVG) and a certificate PDF; the signature is embedded in both, and either file can be verified on its own.
OpenBadgeCredential · vc+jwt · ES256
Institutional identity, key management and account security
Each university has its own key pair and did:web identity; the public key is published in the institution's public did.json document. Key rotation and signing operations are written to the audit log. Accounts are temporarily locked after 10 failed login attempts in a row; all data is backed up encrypted on a regular schedule.
did:web:dijiuni.com:issuers:<code>
Instant revocation and suspension
Revocation or suspension is marked as a single bit in a status list that holds no personal data. Every distributed copy shows as revoked at its next verification.
Bitstring Status List v1.0
Verification Statement
Every PDF certificate carries a block that cannot be removed from the template: verification address, QR, document number, issue date and the first 16 characters of the document digest (SHA-256). The values match those on the verification page.
VC signature + QR + document no + digest
e-Devlet Document Query Service on the institution's behalf
DijiUni provides, for each institution, the query service that e-Devlet calls, so the SEM does not need its own software. It has SOAP and REST endpoints, an IP allowlist and a query log; fields are adapted to the TÜRKSAT specification.
/edevlet/<institution>/BelgeSorgulaService.svc
YÖKSİS application package and approval tracking
A package ready for the YÖKSİS application is produced from the programme record. The YÖK approval number, date and conditions are recorded; no SEM certificate can be issued from an unapproved programme. The approval number is inside the badge and on a public page.
/yok-approvals/<approval-no>
The 11 EK-1 fields as structured data
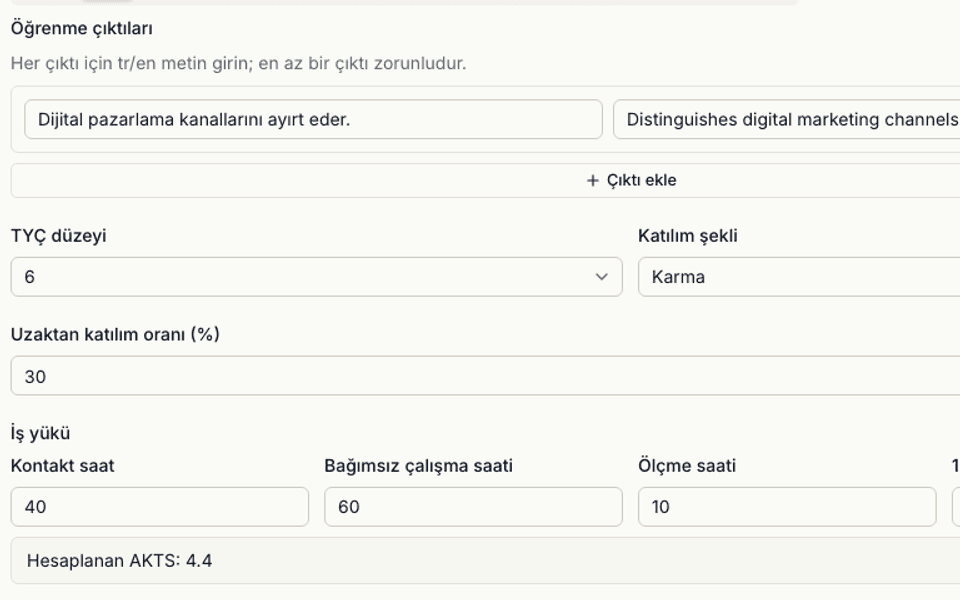
The programme form holds each of the 11 fields separately; the same fields are written into the signed badge's data. ECTS is calculated from the 25-hour workload definition.
JSON-LD · achievement · dijiuni:learningOutcomes[]
Digital wallet
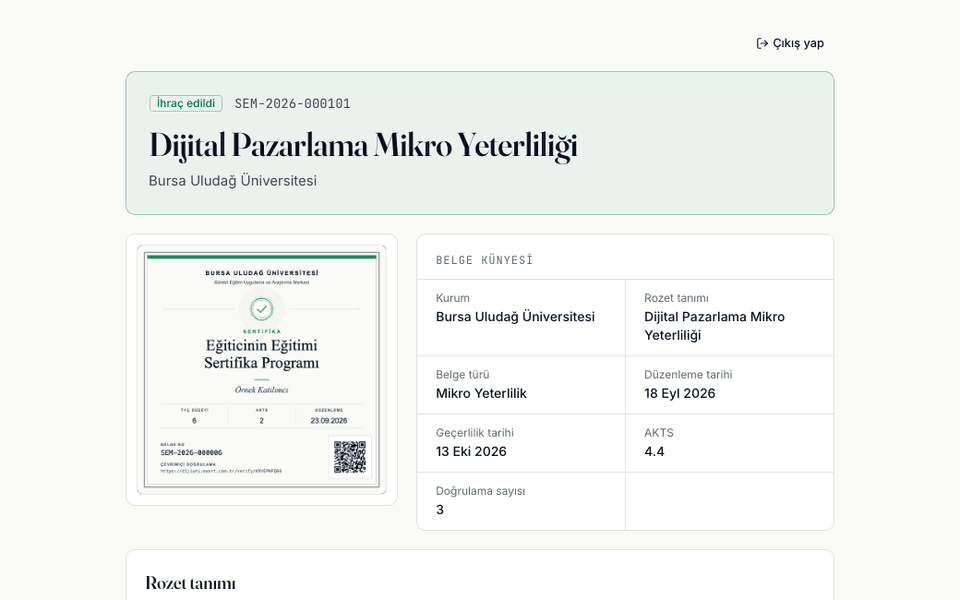
Under the user's control: sign-in by email link, visibility settings, sharing by link and QR, adding to LinkedIn, downloads. For recognition requests it produces a package of the EK-1 PDF, signed data and verification links.
OB 3.0 Host · recognition package
Signature chain and audit log
Approval steps are defined by the institution per document type (e.g. Coordinator → SEM Director → Deputy Rector). The name and title printed on the certificate are taken from the account of the person who actually approved that step, at the moment of approval. Every approval, revocation and correction is recorded with user and time.
Issue requests · Audit log
Attendance and pass rules per programme
Attendance percentage and pass threshold are set per programme; once results are entered, pass status is calculated automatically.
Programme · Cohort · Assessment
KVKK (data protection)
The TCKN is stored encrypted only in the institution's record; the badge carries only a salted hash. Privacy notice and explicit consent are shown on separate screens, and consent records are time-stamped.
credentialSubject.identifier · sha256$…
Accessibility
The verification portal and wallet are designed to WCAG 2.2 AA and pass automated accessibility tests.
WCAG 2.2 AA
Integration
REST API and signed webhooks, Open Badges 3.0 API, import from learning management systems (LMS) by CSV and LTI 1.3, and SAML/OIDC single sign-on for institution staff.
REST · Webhook (HMAC) · LTI 1.3 · SAML/OIDC
Mobile digital wallet app
Credential holders can now also view their badges from a mobile app (Android/iOS): email-link sign-in, offline viewing, Apple/Google Wallet. It shares the same account and data as the web wallet.
Android · iOS (pilot)
Learner record with CLR 2.0
The recognition package now bundles multiple badges into a single signed learning portfolio (Comprehensive Learner Record); each badge keeps its own signature, so the whole set can be verified from one document.
CLR 2.0 · portfolio.clr.jwt
Independently verifiable
Every institution's issuer identity uses the did:web standard. A compliant verifier outside DijiUni can verify a badge's signature independently from the institution's public key, without ever connecting to DijiUni.
did:web:dijiuni.com:issuers:<code>
Passed acceptance testing
All 12 official acceptance criteria in SPEC.md §11 were verified end-to-end with real scenarios — a real signed JWT, a real national ID number, a real e-Devlet SOAP client; no mocks.
SPEC §11 · 12/12 verified
From the product's real screens
Problem → direct solution
Solution map
Each row answers a numbered problem above. The last row is not a problem but a public-sector obligation.
| Problem | How DijiUni solves it | Where | Basis |
|---|---|---|---|
| 01Fake and forged PDFs | The badge and the certificate PDF are produced from the same signed record and signed together with the institution's key; change one character and the signature breaks, so verification reports “Tampered”. | /verify · badge file (PNG/SVG) · certificate (PDF) | Art. 6-g; W3C VC 2.0 YÖK Procedures (opens in a new tab)W3C VC 2.0 (opens in a new tab) |
| 02Verification by phone | Verification in seconds by short code or QR, no account needed. Keyed API for bulk checks. | /verify · POST /api/v1/verify | Art. 9 (duty to verify); Open Badges 3.0 YÖK Procedures (opens in a new tab)Open Badges 3.0 (opens in a new tab) |
| 03Scattered verification pages | One address for all institutions; issuer identity resolves via did:web from the institution's public document. | /verify · /issuers/<code> | Art. 6-g; did:web YÖK Procedures (opens in a new tab)did:web (opens in a new tab) |
| 04Lost certificates | The badge stays in the wallet; the badge image (PNG/SVG), certificate PDF and signed data can be downloaded again together at any time. The institution keeps its record for the legal period, backed up encrypted on a regular schedule. | Wallet › Badge › Download | Art. 4-c (secure, portable, user-controlled); EGESEM Art. 15 YÖK Procedures (opens in a new tab)EGESEM Directive (opens in a new tab) |
| 05Unverifiable LinkedIn entries | “Add to LinkedIn” includes the verification link, which shows live status (valid, revoked). | Wallet › Badge › Share | Art. 6-ğ/h (portability); Open Badges 3.0 YÖK Procedures (opens in a new tab)Open Badges 3.0 (opens in a new tab) |
| 06Missing evidence for recognition | Recognition package: EK-1 PDF + signed data + verification links. If the target institution uses DijiUni, the request lands in its “Recognition requests” queue. | Wallet › Recognition | Art. 9 (traceable, provable) |
| 07Lost EK-1 fields | The 11 fields are structured in the programme form and carried inside the signed badge. | Programmes › EK-1 · badge data | Art. 8, EK-1 |
| 08A separate e-Devlet service per SEM | Document Query Service (SOAP/REST) on the institution's behalf, with IP allowlist and query log. | Settings › e-Devlet · /edevlet/<institution>/… | SEM regulation (01.10.2026); TÜRKSAT Service Integration Protocol AA (opens in a new tab)TÜRKSAT protocol (opens in a new tab) |
| 09No link to the YÖK approval number | The approval number is recorded on the programme and written into the badge; no SEM certificate can be issued from an unapproved programme. | Programmes › YÖKSİS · /yok-approvals/<no> | YÖK letter, 02.07.2026 |
| 10Openly circulating TCKN | TCKN encrypted and kept only at the institution; the badge holds a salted hash. Privacy notice and consent are separate texts. | Badge identity field · Settings › KVKK and legal texts | KVKK TCKN Guide; Board decision 2026/347 KVKK TCKN Guide (opens in a new tab)KVKK 2026/347 (opens in a new tab) |
| 11Off-record signature chain | Approval chain per document type; the name and title printed on the certificate come from the person who actually approved that step, and every step is in the audit log with user and time. | Issue requests · Audit log | Institutional SEM directive (e.g. İTÜ SEM; EGESEM Art. 13) İTÜ SEM Directive (opens in a new tab)EGESEM Directive (opens in a new tab) |
| 12Varying attendance and pass thresholds | Attendance and pass thresholds per programme; pass status is calculated automatically. | Programmes · Cohorts › Attendance / Assessment | Institutional directive; Art. 11 (assessment results reflected in the certificate) |
| 13Revoked certificates in circulation | Instant revocation or suspension via the status list; every copy shows as revoked at its next verification. | Badges › Revoke · status list | W3C Bitstring Status List |
| 14Badges only reachable from a browser | A mobile app (Android/iOS, pilot) sharing the same account brings badge viewing, email-link sign-in and offline viewing to the phone. | Mobile app (pilot) · deep link | SPEC.md §6.5/§10 v2 |
| 15Proving several badges as one package | The recognition package now includes a single signed CLR 2.0 learning portfolio (portfolio.clr.jwt); each badge keeps its own signature. | Wallet › Recognition · GET /wallet/portfolio.clr.jwt | 1EdTech CLR 2.0 |
| 16Verification depends on DijiUni | Institutions' issuer identity uses the did:web standard; any compliant external verifier can verify a badge independently from the institution's public key, without ever connecting to DijiUni. | /issuers/<code>/did.json | did:web |
| 17Independent proof the system's claims hold up | All 12 official acceptance criteria in SPEC.md §11 were verified end-to-end with real scenarios, not mocks. | docs/acceptance-v1.md | SPEC.md §11 |
| —Public accessibility obligation | Verification and wallet screens are designed and tested to WCAG 2.2 AA. | Verification portal · Wallet | Circular 2025/10; WCAG 2.2 Circular 2025/10 (opens in a new tab)WCAG 2.2 (opens in a new tab) |
What it does not do
Honest limits
It does not upload certificates to e-Devlet. e-Devlet stores no certificates; when queried it asks the institution's service. DijiUni provides that service on the institution's behalf.
It does not replace YÖK approval. YÖK grants programme approval through YÖKSİS. DijiUni prepares the application package and tracks the approval number.
It does not by itself give the certificate legal status. Legal status comes from the institution's electronic document directive and from being checkable on e-Devlet. No qualified electronic seal is used.
Sources
Sources
All links were reachable as of September 2026. Details that are not public are not claimed on this page. Most sources are in Turkish.
- e-Devlet Gateway — TÜRKSAT Service Integration Protocol (opens in a new tab)
kamu.turkiye.gov.tr
- e-Devlet Gateway — Barcoded Document Verification (opens in a new tab)
www.turkiye.gov.tr
- 1EdTech — Open Badges 3.0 Implementation Guide (opens in a new tab)
www.imsglobal.org
- W3C CCG — did:web method specification (opens in a new tab)
w3c-ccg.github.io
See the system for yourself
Institutions can sign in and define their first programme; anyone can verify a badge without an account.